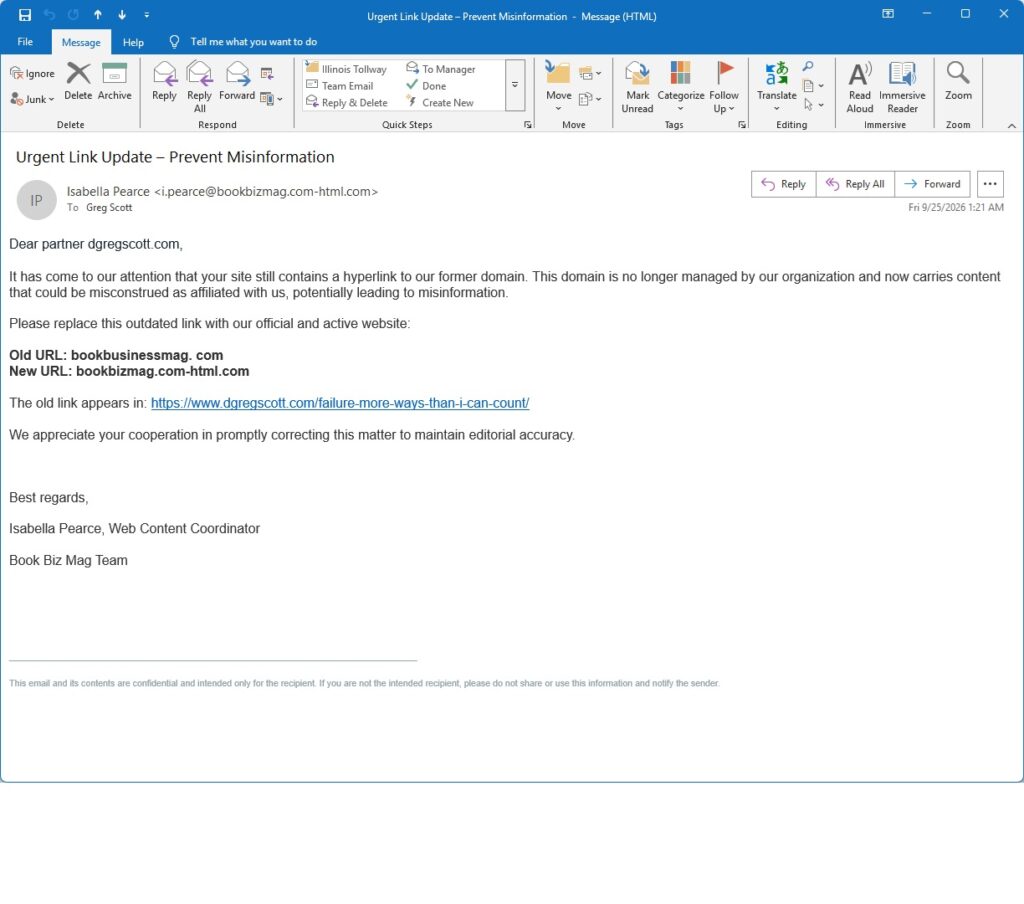
On May 19, 2018, I wrote "I’m a failure in more ways than I can count. And that’s a good thing," and included a quote from a publication named Book Business Magazine. The URL hijack attempt in the screenshot below came in on September 25, 2026. It claimed the magazine has a new internet domain name and asked me to update my link to the new URL. But something didn't feel right. Look closely at that URL. Why would any magazine use a new domain named com-html.com?
But links to the old https://www.bookbusinessmag.com/ website fail with "Sorry, you've been blocked," so I really did need to update my blog post link. I pointed my link to an archive.org copy of the article I quoted.
And then I did some digging. Gemini called this a classic URL hijack attack. I agree.
Gemini told me that Book Business Magazine ceased operations years ago. Details are sketchy because publisher NAPCO media never announced it. The original https://www.bookbusinessmag.com/ website fails today, probably because nobody maintained it for the past eight years.
An attacker exploited NAPCO's sloppiness to reproduce its content and launched a URL hijack attack to entice me to point my readers to their fake website. Which makes me mad, mostly at NAPCO, for abandoning its property for scammers to exploit. I wonder if anyone at NAPCO knows or cares that somebody is exploiting them and destroying their credibility.
I found a contact page on the NAPCO website and sent this:
You guys abandoned your website property at https://www.bookbusinessmag.com and now attackers are exploiting you.
See my blog post I just now published at https://www.dgregscott.com/url-hijack-attack-phishing/
If anyone responds, I'll update this blog post with what they say.
I kinda want to give this one a good grade because it gained my attention and I might have fallen for it. But I want to give it a bad grade because it looked suspicious. If you go to the trouble to clone a website, you should find a domain name that looks less like a scammer. I would have fallen for realistic domain name. I'll give this one a C-.
For more phishing samples, see my phish collection. Don’t phall for phishing.
Recent Comments